Complete PAM Feature Set for Modern Enterprises
Every capability your security team needs to manage privileged access, protect sensitive systems, and maintain continuous compliance, in one unified platform.
Supported Protocols & Asset Types
 Linux
 Windows
 Ubuntu
 Debian
 Red Hat
 SUSE
 Fedora
 Rocky Linux
 Docker
 Kubernetes
 OpenShift
 Rancher
 PostgreSQL
 MySQL
 MongoDB
 Redis
 Oracle
 MariaDBLinuxWindowsUbuntuDebianRed HatSUSEFedoraRocky LinuxDockerKubernetesOpenShiftRancherPostgreSQLMySQLMongoDBRedisOracleMariaDBLinuxWindowsUbuntuDebianRed HatSUSEFedoraRocky LinuxDockerKubernetesOpenShiftRancherPostgreSQLMySQLMongoDBRedisOracleMariaDBLinuxWindowsUbuntuDebianRed HatSUSEFedoraRocky LinuxDockerKubernetesOpenShiftRancherPostgreSQLMySQLMongoDBRedisOracleMariaDB
 Elasticsearch
 Cassandra
 Snowflake
 Kafka
 Splunk
 Vault
 IBM Cloud
 AWS
 Azure
 Google Cloud
 VMware
 Terraform
 Ansible
 GitHub
 GitLab
 Okta
 Anthropic
 OpenAIElasticsearchCassandraSnowflakeKafkaSplunkVaultIBM CloudAWSAzureGoogle CloudVMwareTerraformAnsibleGitHubGitLabOktaAnthropicOpenAIElasticsearchCassandraSnowflakeKafkaSplunkVaultIBM CloudAWSAzureGoogle CloudVMwareTerraformAnsibleGitHubGitLabOktaAnthropicOpenAIElasticsearchCassandraSnowflakeKafkaSplunkVaultIBM CloudAWSAzureGoogle CloudVMwareTerraformAnsibleGitHubGitLabOktaAnthropicOpenAI
Authentication: Verify Every Identity
Block unauthorized access with enterprise-grade identity verification. OmniPriv integrates seamlessly with your existing identity infrastructure while adding layers of protection that prevent credential abuse, account takeovers, and unauthorized entry.
Built-in CAPTCHA
Configurable CAPTCHA protects login pages from automated brute-force attacks.
LDAP / AD Integration
Bidirectional sync with Active Directory and LDAP directories. Automatic user and group provisioning.
Single Sign-On (SSO)
SAML 2.0, OAuth 2.0, and OpenID Connect support for seamless enterprise identity integration.
Multi-Factor Authentication
TOTP (Google Authenticator), FIDO2/WebAuthn hardware keys, SMS/email OTP, and push notifications.
RADIUS Support
Manage network device authentication through the industry-standard RADIUS protocol.
Conditional Access
Context-aware policies based on user location, device posture, time of day, and risk score.
Account Management: Full Credential Lifecycle
Eliminate the credential hygiene problem that plagues enterprise IT. OmniPriv automates every aspect of privileged account management, from discovery to rotation to deprovisioning, so your team focuses on security, not manual credential tasks.
Asset & Account Discovery
Automatically discover privileged accounts across your entire infrastructure, on-prem, cloud, and hybrid.
Credential Rotation
Rotate passwords, SSH keys, and API tokens on a schedule or on-demand, for thousands of assets simultaneously.
Encrypted Credential Vault
Store credentials in an encrypted vault. No user ever sees raw passwords, they authenticate through OmniPriv.
Credential Push
Push updated credentials directly to target assets after rotation. No manual steps, no outages.
Break-Glass Access
Emergency access procedures with mandatory approval, time limits, and full session recording.
Account Lifecycle Management
Provision, deprovision, and modify privileged accounts across all systems from a single control plane.
Audit & Compliance: Full Traceability
Every privileged action leaves a permanent, tamper-proof record in OmniPriv. Compliance teams can generate audit reports in minutes, security teams can investigate incidents in real time, and executives get the visibility they need to manage risk.
HD Session Recording
Record every privileged session in text (searchable) or video format. Replay any session from any point in time.
Real-Time Session Monitoring
Watch live sessions, send notifications to users, or terminate suspicious sessions in one click.
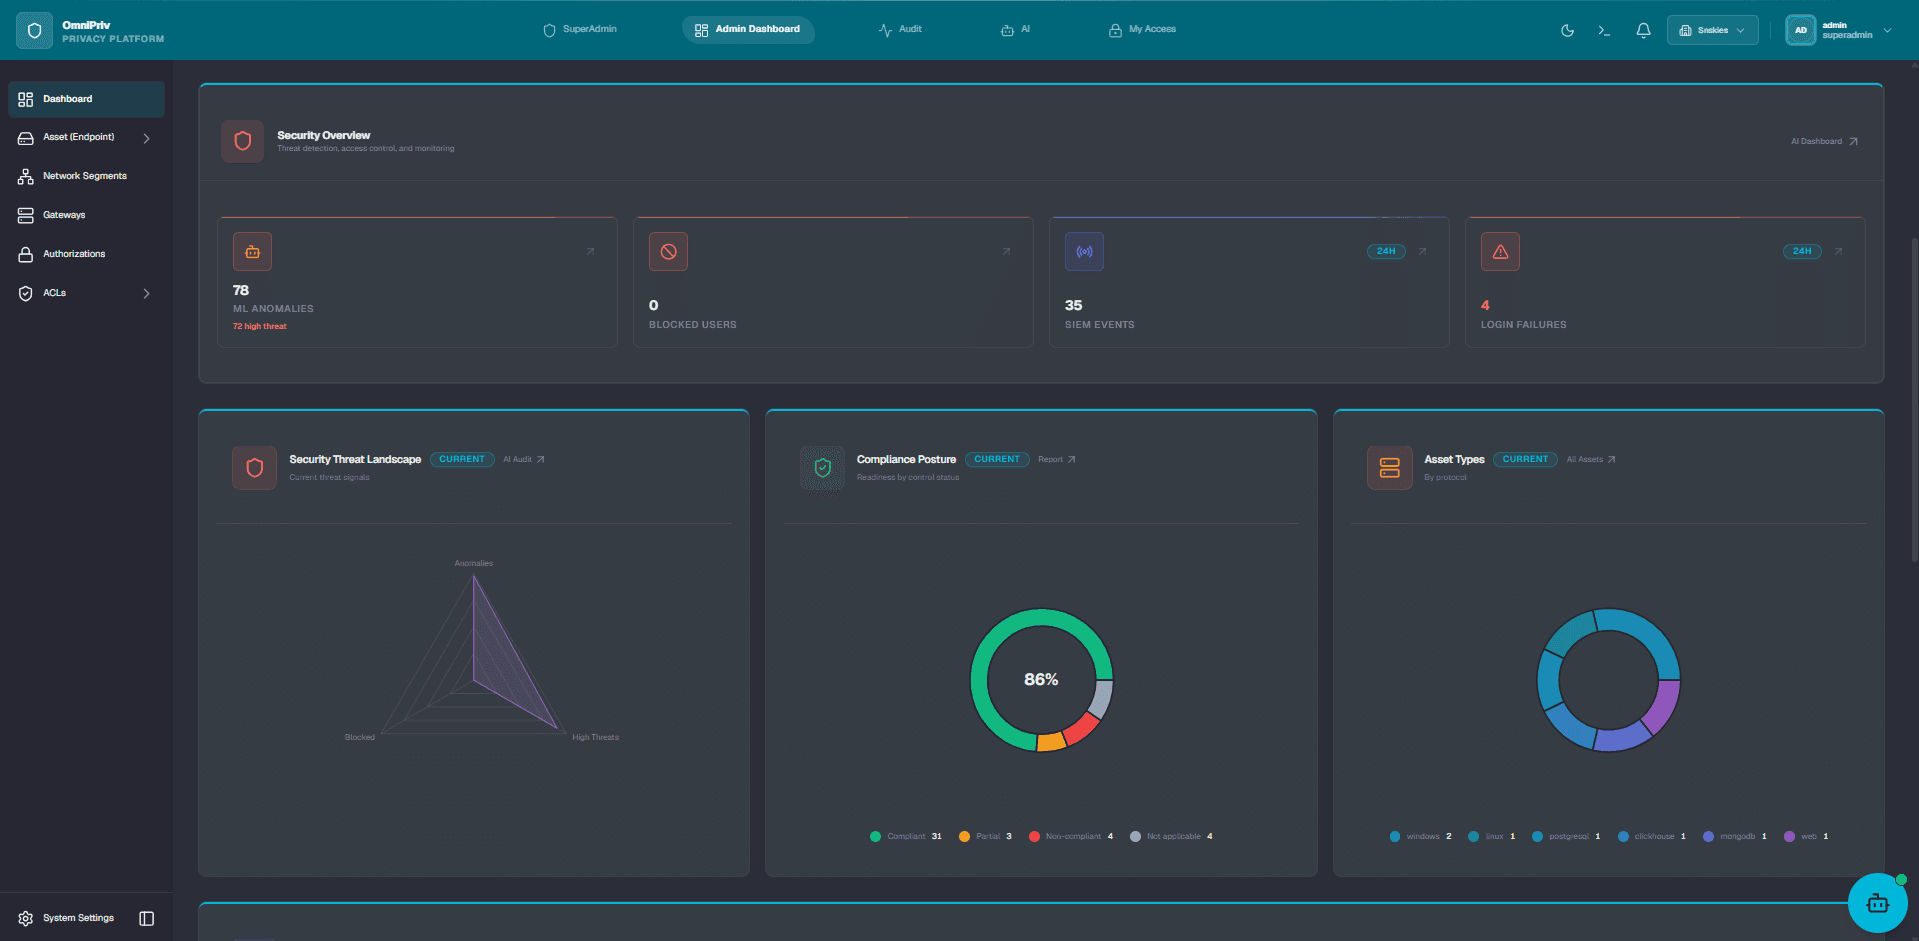
Analytics Dashboards
Executive-level risk dashboards showing access patterns, anomalies, and compliance status.
Command History
Full keystroke logging and command execution history for every SSH and terminal session.
SIEM Integration
Stream all events to Splunk, IBM QRadar, Elastic SIEM, or any syslog-compatible system.
Compliance Reports
One-click audit reports pre-formatted for SOC 2, ISO 27001, NIST SP 800-53, HIPAA, PCI DSS and SOX 404.
AI & Automation: Intelligence on Every Privileged Action
OmniPriv's AI-PAM engine scores behaviour on every privileged action and governs autonomous agents through the same policy engine that governs people. Detection, approval and enforcement happen inside the platform, not in an analytics product bolted onto it.
Explore the AI-PAM engineML Anomaly Detection
Machine-learning behavioural scoring runs on every privileged login and session, catching lateral movement, credential harvesting and brute force in real time.
Behavioural Analytics
AI keystroke-dynamics and per-agent baselines flag impossible travel, off-hours access and deviation from learned behaviour.
Adaptive MFA Step-Up
Keystroke rhythm, speed and pattern are compared against the identity's baseline at login, drift triggers an MFA challenge automatically.
AI Agent Governance
Every MCP agent gets a verifiable identity, tool allowlist and data scope. All 53 MCP tools sit under policy rather than under a borrowed human login.
Human-in-the-Loop Approval
High-risk agent actions, drop table, delete cluster, transfer funds, pause for explicit human approval before they execute.
Prompt-Injection Guard
Even when an LLM's reasoning is manipulated, every tool call is re-verified against deterministic policy before it is allowed to run.
Agent Session Audit Trail
A full forensic trace from human to agent to MCP server to tool to resource, with decision, privilege level and duration recorded.
Automated Threat Response
Each session is scored 0-1 across 39 features and escalates in tiers: dashboard alert, then admin alert, then automatic block on a 10-second sweep.
Frequently Asked Questions
Common questions about deploying and running OmniPriv.
OmniPriv covers authentication, authorization, privileged account management, session audit and AI-driven controls in one platform. That means MFA and SSO, role-based and just-in-time access, credential vaulting and rotation, full session recording, and an AI engine that scores behaviour on every privileged action.
No. OmniPriv works with the directory and identity infrastructure you already run: Active Directory and LDAP for directory sync, and SAML 2.0, OAuth 2.0 or OpenID Connect for single sign-on, with RADIUS for network devices. It adds privileged access controls on top of your identity provider rather than replacing it.
RBAC decides what an identity is allowed to reach. Just-in-time access decides when, it provisions time-limited access for a specific task and revokes it automatically when the window closes.
The result is no standing privilege: an account that is compromised outside an approved window has nothing to use.
Yes. Passwords, SSH keys and API tokens can be rotated on a schedule or on demand, and the updated values are pushed directly to the target assets. No user ever sees the raw credential, they authenticate through OmniPriv instead.
Every MCP agent is given a verifiable identity, a tool allowlist and a data scope, so it operates under policy rather than through a borrowed human login.
High-risk actions pause for explicit human approval, and each tool call is re-verified against deterministic policy before it runs, even when the model's own reasoning has been manipulated. Every session leaves a forensic trail from human to agent to tool to resource.
Audit reporting covers SOC 2, ISO 27001, NIST SP 800-53, HIPAA, PCI DSS and SOX 404. Every privileged action is recorded with the identity, the access decision, the privilege level and the duration, so evidence is available without reconstructing it after an incident.